
Privileged Access & Data Security for Fintech
Adaptive gives fintech engineering, support and AI agents just-in-time access to production systems, with cardholder and account data masked and every action audited.
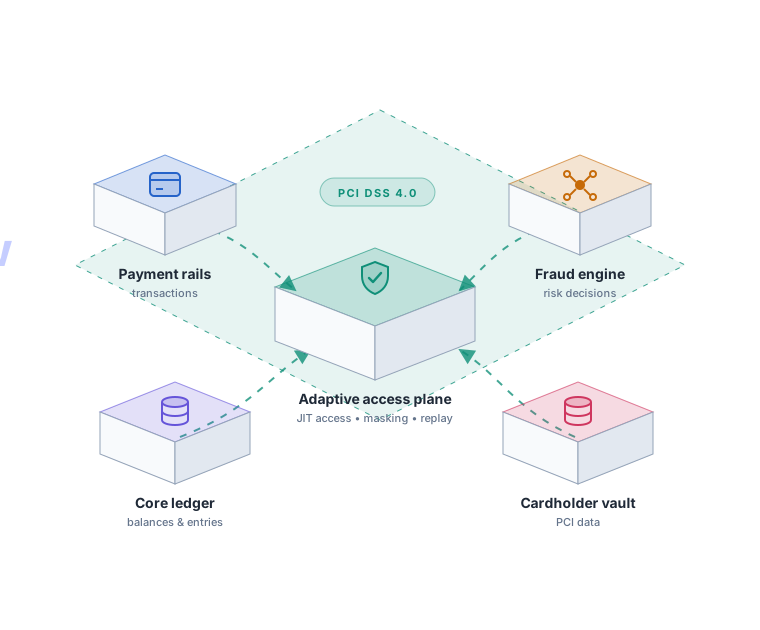
Fintechs move fast on cloud-native infrastructure while being held to bank-grade regulation. Every engineer, contractor and automated agent touching production databases, payment systems or ledgers is a compliance and fraud risk.
Fintech teams juggle PCI DSS, SOC 2, NYDFS, DORA and partner-bank due diligence at the same time. Shared database credentials, long-lived SSH keys and standing admin access make it hard to prove who touched which account record and why. Sponsor banks and auditors expect evidence on demand, and AI agents now querying production data add a new class of identity that legacy PAM tools were never built to govern.
Adaptive makes least-privilege the default for fintech
Adaptive brokers every connection to databases, Kubernetes clusters and servers through identity-aware, just-in-time access tied to your SSO. Sensitive fields such as card numbers, account numbers and PII are masked in flight, so engineers, support staff and agents only see what they need. Every query and command is recorded in immutable audit logs, turning PCI DSS, SOC 2 and partner-bank evidence requests into a report instead of a project.
How Adaptive helps
Just-in-Time Production Access
Replace standing credentials with time-bound, approval-gated access to production. Access expires automatically, removing the long-lived privileges attackers and insiders exploit.
Mask Cardholder and Account Data
Dynamically mask PANs, account numbers and customer PII at the access layer, keeping sensitive data out of terminals, BI tools and AI agents while workflows keep running.
Audit-Ready Evidence
Query-level logs, session recordings and access reviews give auditors and sponsor banks a complete record of who accessed what, when and under which approval.
 |
 SOC2 Type II

