
Access Governance for Enterprise Technology
Adaptive helps enterprise software and cloud companies govern privileged access for thousands of engineers, vendors and AI agents across multi-cloud infrastructure.
Enterprise technology companies run sprawling, multi-cloud estates with many teams, contractors and automated agents all needing access to production. Enterprise customers expect proof that their data is protected.
As engineering organizations grow, access grows faster than anyone can review it. Shared bastion hosts, static keys and per-tool permission models create blind spots across AWS, GCP, Azure, Kubernetes and dozens of databases. Security questionnaires, customer audits and certifications demand consistent controls and evidence, while developers expect access that does not slow them down.
One control plane for every privileged identity
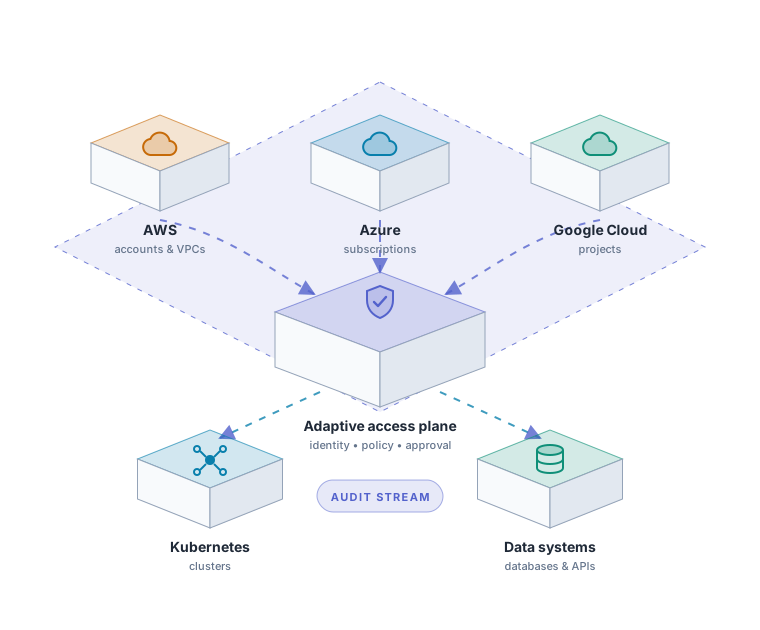
Adaptive unifies access to databases, servers, clusters and cloud resources behind a single identity-aware control plane. Integrate with your IdP, define policies once and grant just-in-time access through Slack or the CLI. Vendor and agent access is scoped to specific resources and fully audited, and Adaptive can be deployed in your own VPC to meet enterprise data residency requirements.
How Adaptive helps
Centralized Policy Across Clouds
Define access policies once and enforce them across every cloud, cluster and datastore, replacing fragmented per-tool permissions with a single source of truth.
Developer-Friendly Just-in-Time Access
Engineers request access from the tools they already use and get it in seconds after approval, without handling credentials or waiting on tickets.
Scoped Vendor and Agent Access
Give contractors, vendors and AI agents temporary access to exactly the resources they need, with every command and query logged and alerts on sensitive data access.
Evidence for Customer Audits
Answer security questionnaires and certification audits with access reviews, session recordings and immutable logs that are always up to date.
 |
 SOC2 Type II

